Fail-closed
by design.
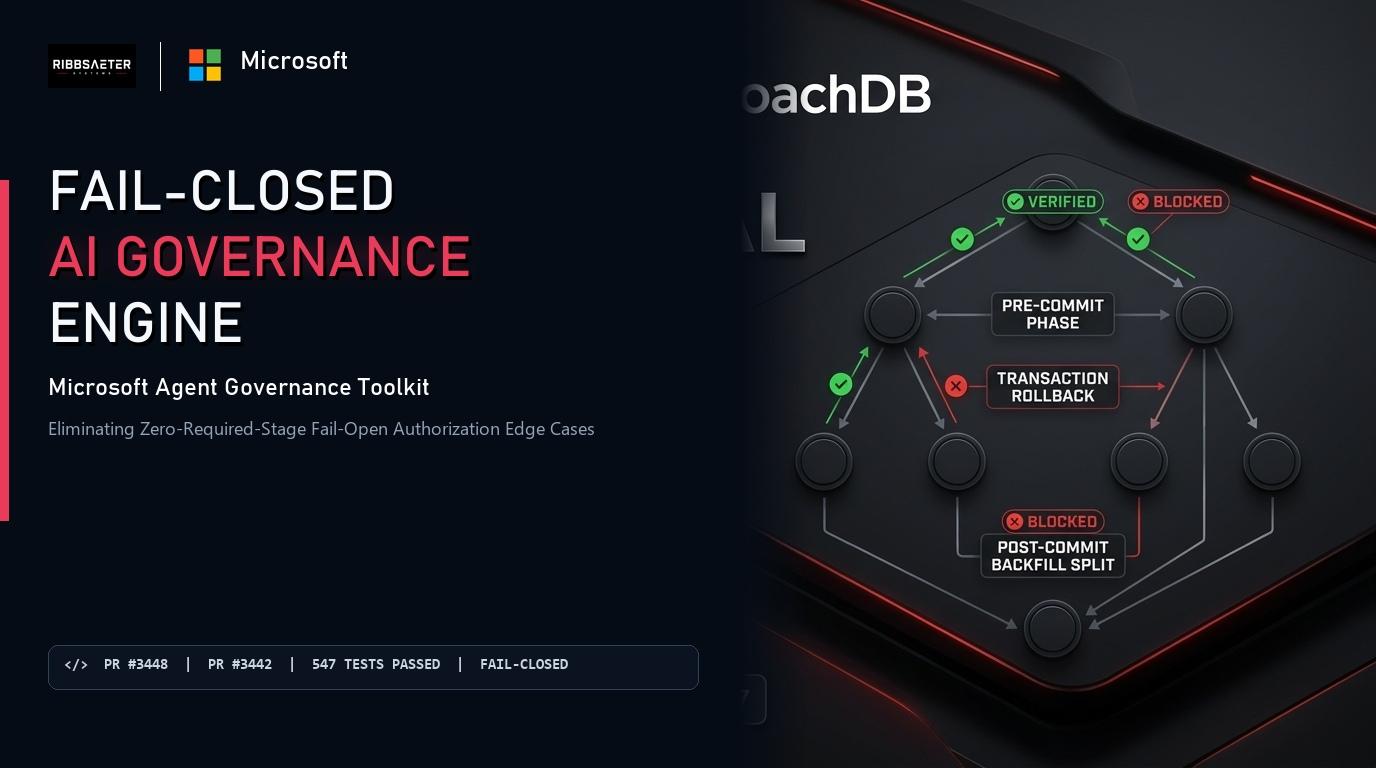
Two merged contributions to Microsoft's Agent Governance Toolkit: fail-closed approval-chain authorization and policy validation that rejects false success.
2
merged PRs
547
tests passed
2
human approvals
Microsoft
upstream repository
01 · The problem
Mathematically valid.
Operationally unsafe.
An approval chain could be configured with zero required stages. The evaluator used set containment to decide whether every required stage had completed.
Because the empty set is a subset of every set, the condition evaluated as satisfied. An optional, non-advisory ALLOW decision could therefore influence authorization even though no meaningful required approval stage existed.
In a governance system, incomplete policy configuration should never become authorization.
02 · Failure mode
From vacuous truth to an explicit invariant
Before · implicit set logic
required_stages = ∅
∅ ⊆ completed_stages  →  true
After · explicit guard
required_stages.length == 0
→ deny resolution and execution
03 · The correction
Deny ambiguous policy state.
- 01
Reproduced the zero-required-stage chain with an optional non-advisory ALLOW result.
- 02
Traced the decision path to empty-set containment and identified vacuous truth as the source.
- 03
Added an explicit guard that denies the chain before general completion logic executes.
- 04
Verified that resolution, request state, and execution authorization all remain denied.
- 05
Kept the upstream patch focused for maintainable review and cross-implementation consistency.
04 · PR #3442 · Policy validation
Reject tests that prove nothing.
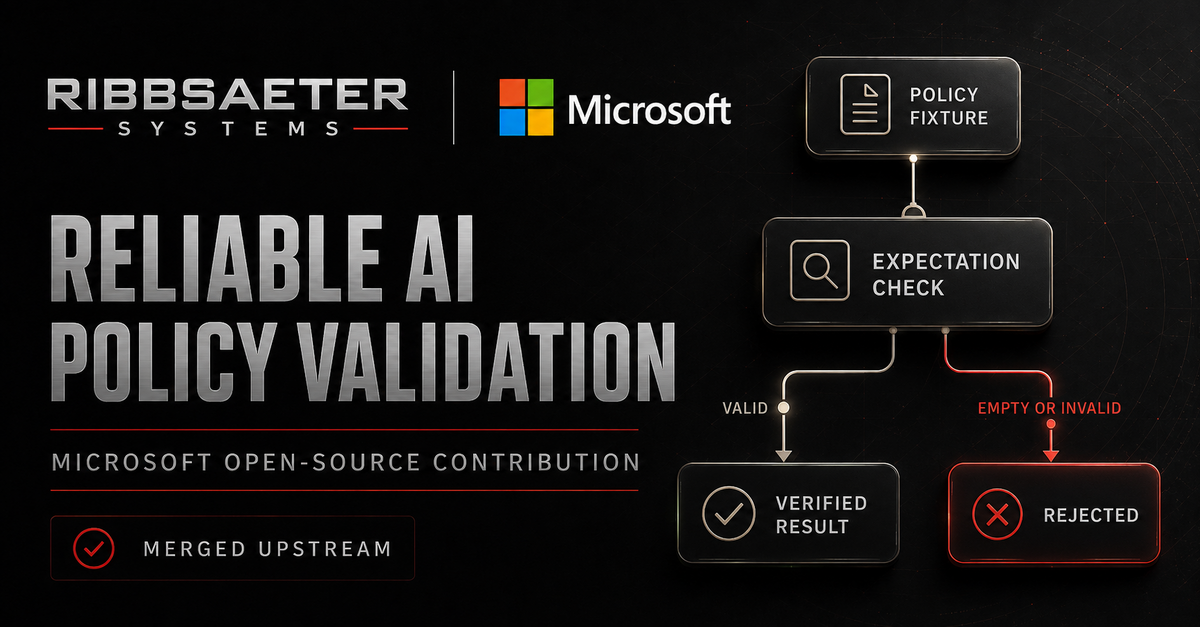
Policy fixtures without meaningful expectations could complete without asserting an outcome, allowing an empty or invalid suite to report false success.
The merged validation change requires at least one non-null expectation, rejects invalid fixtures before execution, and ensures an empty replay report cannot be classified as successful.
Rejected
Empty or null-only expectations
Verified
Meaningful assertion required
05 · Public evidence
Verified beyond the local return value
Merged contributions
2 upstream PRs
Human review
Both approved
Approval protocol
26 tests passed
Policy validation
521 passed · 2 skipped
PR #3448
Zero required stages → deny
PR #3442
Empty fixtures → rejected
Security posture
Fail closed · no false pass
Repository
Microsoft Agent Governance Toolkit
Engineering principle
Critical invariants should be explicit—not accidental consequences of general-purpose logic.
Independent open-source contribution by Ribbsaeter Systems. No partnership or employment affiliation is implied.